Back to Blog


Monica Jansen
Nov 2, 2026
How to Secure Your Website from Cyber Threats
Cyber threats can target different parts of your website, from its software and login areas to its forms and databases.
A single weak point can be enough to put sensitive information, website functionality, or visitor data at risk.
For that reason, effective website security requires a broader approach rather than focusing on every possible threat in isolation.
In this guide, we’ll cover how to assess your website’s security, reduce its attack surface, and protect it from cyber threats.
- What Is Website Security?
- Common Website Security Threats
- Understanding Your Website’s Attack Surface
- Protecting Your Website from Cyber Threats
- How to Check Your Website Security
- Responding to a Security Incident
Follow along!
What Is Website Security?
Website security refers to the measures and practices used to protect a website from cyber threats, unauthorized access, and other malicious activity.
It covers the different parts that keep a site running, including:
- Software
- Server
- User accounts
- Stored data
- Third-party components
A weakness in any of these areas can create an opportunity for attackers to interfere with the website or gain access to information.
However, website security is not a one-time setup. New vulnerabilities can emerge as software changes, integrations are added, and attackers develop new methods.
That’s why understanding the threats a website can face is an important part of knowing where its security may be tested.
Common Website Security Threats
Cyber threats can reach a website in several ways, depending on what an attacker is able to exploit.
Some target the website or its underlying systems directly, while others take advantage of compromised credentials or malicious software.
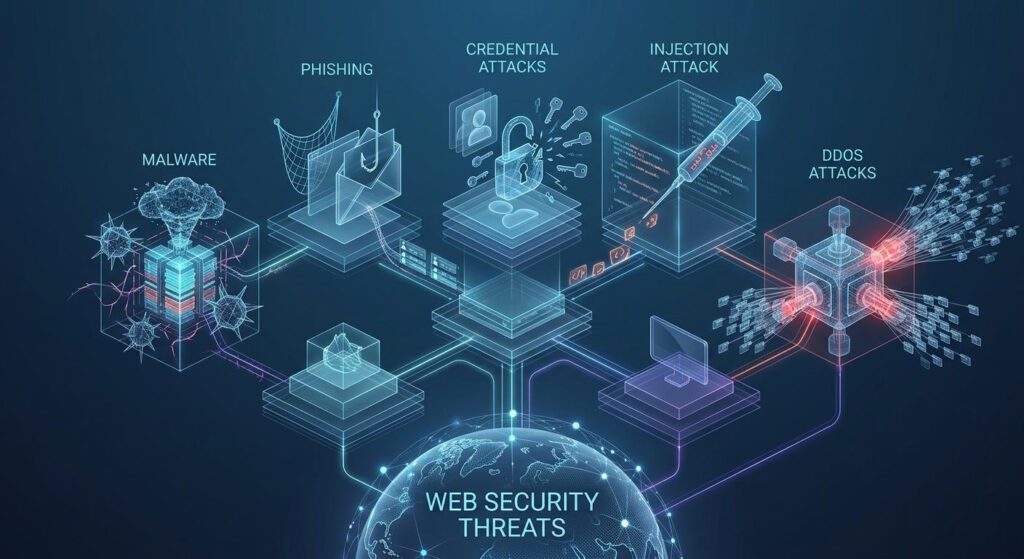
Among the most common ones are:
Malware
Firstly, malware can affect both a website and the systems supporting it.
Once introduced, it may steal information, alter files, redirect visitors, or interfere with normal operations.
More disruptive forms include ransomware, which can encrypt important files and prevent them from being accessed until a payment is provided.
Phishing
Next, phishing relies on deception rather than directly exploiting a technical vulnerability.
Fraudulent emails or messages may imitate a familiar company, colleague, or service to obtain login details or encourage someone to open a harmful link or attachment.
If the attempt succeeds, the stolen information can provide a way into website accounts or connected systems.
Credential Attacks
Similarly, website accounts can be compromised when login details are weak, reused, stolen, or still set to their default values.
For example, credentials exposed in a previous data breach may be tested elsewhere in case the same combination has been reused.
A successful match can give an attacker access to the account, potentially allowing them to make changes or reach protected information.
Injection Attacks
In addition, weaknesses in a website’s code can provide another point of entry.
SQL injection takes advantage of such vulnerabilities to manipulate database queries, and it can expose, change, or delete stored information.
On the other hand, cross-site scripting (XSS) can introduce malicious code that runs in a visitor’s browser, putting user data at risk.
DDoS Attacks
Lastly, a website doesn’t have to be breached for an attack to affect it.
For instance, DDoS attacks can overwhelm a site or server with large volumes of traffic or requests.
As available resources become overloaded, performance may deteriorate until legitimate visitors struggle or are completely unable to reach the site.
Understanding Your Website’s Attack Surface
Cyber threats can affect more than one area of a website, which makes the overall scope of possible attacks important to understand.
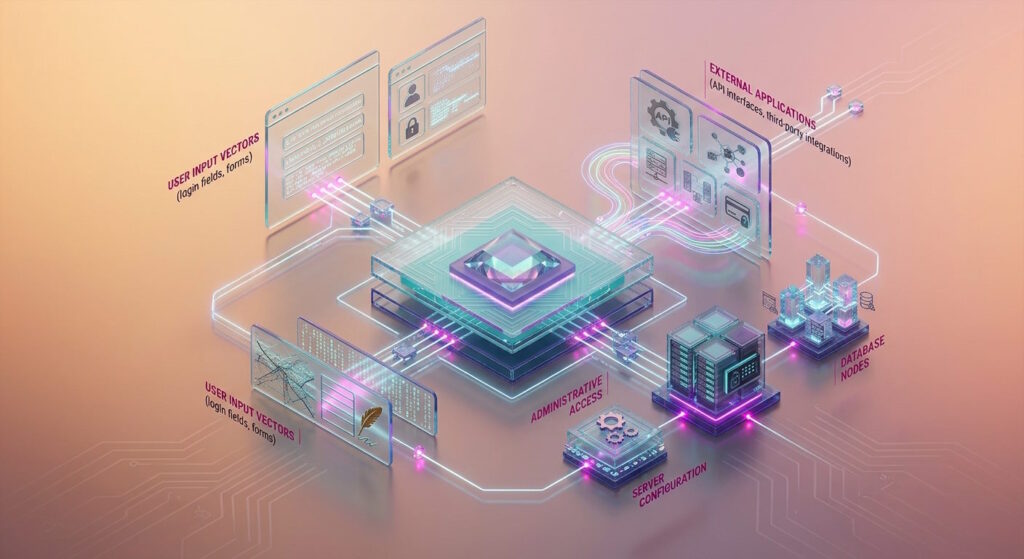
Your website’s attack surface includes all the points that could potentially be targeted or exploited in a cyberattack.
It can include everything from software and user accounts to servers, APIs, and other systems connected to your site.
The larger the attack surface becomes, the more potential entry points there are to manage and protect.
What Can Expand Your Attack Surface
Over time, your attack surface can grow alongside your website:
- New features: They often bring additional software, accounts, or connections that increase the number of elements exposed to potential threats.
- Third-party tools and integrations: These can expand it further, particularly when they connect to important parts of your site or its data.
- APIs: The same applies to APIs and development or staging environments that remain accessible.
Meanwhile, older elements can become a concern as well.
Forgotten subdomains, unused accounts, and services that are no longer needed can stay active long after they have stopped serving a purpose.
How to Reduce Potential Entry Points
In practice, to reduce your attack surface, you need to:
- Create an inventory of everything connected to your website, including software, accounts, integrations, and services.
- Identify what is still necessary and remove or disable anything you no longer use.
- For anything that needs to remain, you should limit access to only the people and systems that actually require it.
- Additionally, it’s worth reviewing how different parts of your website connect to each other. If you limit unnecessary connections, you can prevent a weakness in one area from providing access to others.
- Finally, you should update your inventory regularly as your website changes.
In this way, you can review new additions as they are introduced so they don’t become forgotten parts of your attack surface.
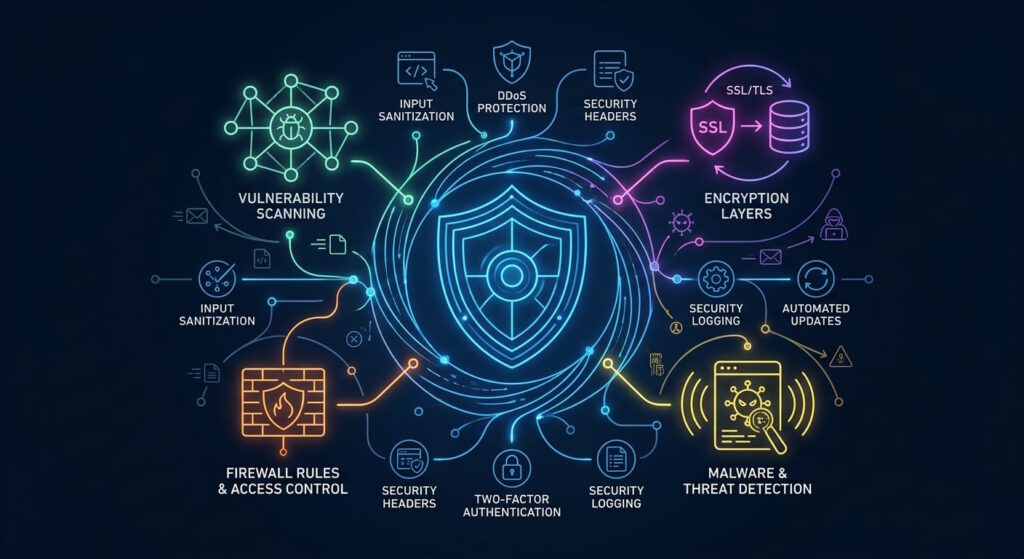
Protecting Your Website from Cyber Threats
Reducing your attack surface limits the opportunities attackers have to target your website.
However, the parts that remain still need appropriate protection.
The right safeguards depend on the role each area plays and the risks it faces.
Public-Facing Pages and Forms
To start, pages that accept input from visitors need particular attention because they provide a direct way for data to enter your website.
For example, login pages, contact forms, and search fields should only accept the type of information they are designed to handle.
To limit the risk, input validation can block data that doesn’t match the expected format, while rate limiting can restrict the number of login attempts within a set time period.
Where file uploads are available, you should place restrictions on file types and sizes to further reduce the chances of harmful content reaching your website.
Accounts and Access
Next, user accounts need safeguards against unauthorized logins in the following ways:
- Use strong, unique passwords and multi-factor authentication (MFA) to make it harder for attackers to gain access using stolen or compromised credentials.
- Limit your permissions to what each user actually needs.
- Only give administrator access to people who require full control over the website.
Where possible, login activity should also be monitored for repeated failed attempts, unfamiliar locations, or logins at unusual times.
Hosting and Network
Beyond user accounts, the infrastructure supporting your website needs to be secured against network-based threats.
Your hosting environment should only expose the ports and services required for your website to function, with sensitive resources kept inaccessible to unauthorized users.
For example, firewalls can filter unwanted connections, while network rules can restrict which systems are able to communicate with each other.
In addition, you should monitor traffic for sudden spikes or unusual patterns to identify potential attacks before they cause wider disruption.
Third-Party Connections
Lastly, any external service connected to your website can introduce risks outside your direct control.
Before adding a new integration, it’s worth checking what data it can access and which permissions it requires.
Once connected, you should review the access levels periodically and remove any that are no longer necessary.
Also, API keys and other credentials should be stored securely and replaced if there is any reason to believe they have been compromised.
How to Check Your Website Security
Regular assessments can help establish how well your website is currently protected.
A website security check can reveal vulnerabilities, configuration issues, and other problems that might otherwise go unnoticed. Here are the steps you can take to assess your own platform:
- Run a website security scan: A vulnerability scanner can flag outdated software, malware, known security flaws, and configuration issues that require attention.
- Check HTTPS and your SSL certificate: Make sure the certificate is valid and every page uses HTTPS, with HTTP traffic automatically redirected to the secure version.
- Check your security headers: Missing or incorrectly configured headers can leave browsers without important safeguards against attacks such as cross-site scripting.
- Review user accounts and permissions: Check who currently has access to your website and whether their permissions still match their role. Old accounts and privileges that are no longer needed should be removed.
- Look for unexpected changes: Unfamiliar files, modified pages, unusual redirects, or other unexplained activity can indicate that your website has been compromised.
- Consider penetration testing: A controlled simulated attack can uncover weaknesses that automated checks may miss and show how well your existing protections hold up.
Responding to a Security Incident
Even with multiple security measures in place, no website is completely immune to cyber threats.
For that reason, it’s important to have a clear plan for how you will respond if you detect a breach or other security incident.
The plan should cover:
- How to identify which systems and data were impacted
- Isolate compromised areas
- Notify the relevant people
Once the immediate threat is contained, clean backups can be used to restore affected data or systems.
Any credentials that may have been exposed should also be replaced before normal operations resume.
Afterwards, you should review how the incident occurred to help you address the vulnerabilities involved and reduce the chances of the same problem happening again.
Conclusion
Cyber threats will continue to evolve, and your website needs to evolve along with them.
By taking a proactive approach, you can address any weak points before they are exploited and respond quickly if an incident occurs.
Ultimately, website security is an ongoing effort. Consistent action is what keeps emerging threats from causing serious damage.
Author
Monica Jansen
Monica Jansen is a seasoned tech writer focused on web hosting and cybersecurity. She loves doing deep dives and whittling down difficult topics into simple and succinct concepts. Whether she is covering firewalls or different hosting plans, she always strives to provide clear guides that website owners of all skill levels can follow.
Add your comment
Get content delivered straight to your inbox
Your data.
Your choice.
Work with the best of the best — your projects deserve it.